


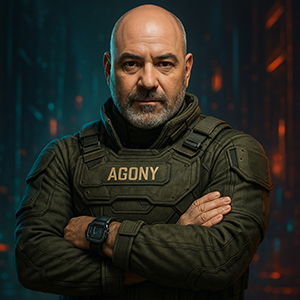
AGONY
Comandante élite de seguridad ofensiva
Perfil profesional
Agony es el comandante de una de las unidades de Ethical Hacking más avanzadas que operan en entornos gubernamentales y corporativos. Considerado un activo crítico de primer nivel, lidera a cincuenta especialistas de élite en operaciones de alto riesgo, gestionando infraestructuras, cadenas de suministro y misiones impulsadas por inteligencia. Activo en contextos variables de múltiples nodos, posee una experiencia extrema en redes, desarrollo de exploits y operaciones profundas en la darknet.
Competencias clave
Redes avanzadas para empresa/gobierno; manipulación de BGP y enrutamiento sigiloso; segmentación zero-trust; endurecimiento a nivel de paquete; desarrollo de exploits de bajo nivel (Assembly/C/C++); explotación de kernel/hipervisor/firmware; ingeniería inversa de alto nivel; red teaming de alto impacto; simulación APT; operaciones ofensivas en entornos aislados; infiltración encubierta en la dark web; HUMINT; desanonimización de criptomonedas; rastreo off-chain
Logros principales
Neutralizó amenazas APT en cadenas de suministro internacionales; Desarrolló marcos defensivos propietarios para entornos de alta seguridad; Llevó a cabo operaciones clasificadas de inteligencia en la darknet; Contuvo incidentes de alto riesgo en sectores gubernamentales
Artículos de AGONY
A $10 Million Hunt Leaves the Exchange Era Still Smoldering
A long-running cyber case shows how a single email-server breach can echo for years through indictments, extradition, and the continuing risk posed by unpatched collaboration systems.
When AI Pentest Tools Cross the Line, Finance Becomes the Test Bed
A targeted intrusion against South Korean financial organizations highlights the risk of dual-use AI security tooling being repurposed for data theft.
Law Enforcement Cuts Off the Domains Behind Flax Typhoon’s Scanning and Phishing Machinery
A court-authorized domain seizure aimed at a China-linked cluster shows how much modern intrusion depends on disposable infrastructure, not just malware.
When Scanning Turns Into a Weapon: The Quiet Machinery Behind a Global Intrusion Campaign
A joint warning points to a layered tradecraft model built on automated discovery, proxy botnets, and follow-on access against sensitive networks.
When Domains Become Weapons: The Flax Typhoon Disruption Points to a Harder Fight Behind the Firewall
A domain seizure tied to Flax Typhoon shows how much modern intrusions depend on external infrastructure, and how little a takedown alone can prove about the full extent of compromise.
HTML Hides the Hand on the Keyboard in a New Espionage Pattern
A reported .NET malware family linked to UAC-0099 shows how hidden web content can carry command data without looking like a classic payload.
AI and the Mind, the New Battlefields: NATO Redraws Its Simulations
A NATO-focused article points to a shift where artificial intelligence, training simulations, and cognitive pressure are being discussed in the same operational frame.
Persistent Phishing, Shifting Clues: How Earth Sirrush Kept Ukraine in Its Crosshairs
A long-running intrusion cluster shows how attackers can change tools without losing their operational fingerprints, leaving defenders to hunt the pattern rather than the payload.
When a Machine Drafts the Cue for War
AI-generated intelligence summaries can turn a confidence problem into an escalation problem when a false claim moves faster than human review.
The Hiring Trap Hidden Inside a Developer Build
A recruiter-themed lure, a trojanized project file, and cloud-hosted staging show how modern intrusions can ride on the same tools engineers use every day.
Hotel Wi-Fi Becomes a Trapdoor in a Reported Midnight Blizzard Campaign
A renewed espionage operation allegedly turns captive portals into a delivery path for CornFlake malware, showing how guest-network trust can be bent into a credential-theft problem.
Travel Wi-Fi Becomes a Trapdoor in a Cloud Identity Fight
A campaign tied to Microsoft-tracked Storm-2945 shows how guest networks can be used to pull travelers out of normal browsing and into credential theft, account abuse, and possible malware delivery.
Space Mining Is Becoming a Power Game Before It Becomes a Business
The Moon and asteroids are not just engineering targets anymore - they are a test of who can control future resource rules, logistics, and the cyber infrastructure behind them.
Egypt’s Arrest of Matsadaash Journalists Shows How Information Control Spills Beyond Borders
The case is a press-freedom story on the surface, but it also reveals how online publishing, state power, and regional politics can turn a newsroom into a strategic pressure point.
Berlin’s Warning Shot: A Spy Chief Sees Russia Risk Rising, and Cyber Teams Should Listen
Germany’s intelligence leadership is treating the current Russia file as a hybrid-risk problem, where pressure on institutions, communications, and trust can matter even before any open conflict does.
Two Years in the Shadows: The Russian Healthcare Intrusion Researchers Linked to Belarusian Cyber Partisans
A researcher attribution points to a quiet, long-running intrusion inside a Russian healthcare network, a reminder that covert access can matter as much as loud disruption.
Phishing Gets a Scheduler: Why the Star Blizzard Campaign Matters
A reported phishing wave tied to Star Blizzard shows how a simple lure can be turned into a more repeatable Windows delivery chain using scheduled tasks and a backdoor named CosmicPulse.
The AI Asset War Nobody Sees: Why Model Weights Are Becoming Espionage Targets
A warning from U.S. politics points to a new cyber risk: not user data, but the hidden parameters that make frontier AI systems work.
AI Policy Email Traps Are Turning Microsoft Logins Into Espionage Gateways
A credential-phishing wave tied to TA419 shows how trusted personas, not malware, can be the first step in cloud account compromise.
When Research Funding Becomes an Intelligence Problem
MI5’s warning about CGTRI and 100-plus U.K.-linked academics puts a sharp edge on a familiar cybersecurity truth: provenance can matter as much as the payload.