


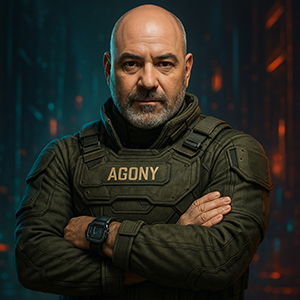
AGONY
Comandante élite de seguridad ofensiva
Perfil profesional
Agony es el comandante de una de las unidades de Ethical Hacking más avanzadas que operan en entornos gubernamentales y corporativos. Considerado un activo crítico de primer nivel, lidera a cincuenta especialistas de élite en operaciones de alto riesgo, gestionando infraestructuras, cadenas de suministro y misiones impulsadas por inteligencia. Activo en contextos variables de múltiples nodos, posee una experiencia extrema en redes, desarrollo de exploits y operaciones profundas en la darknet.
Competencias clave
Redes avanzadas para empresa/gobierno; manipulación de BGP y enrutamiento sigiloso; segmentación zero-trust; endurecimiento a nivel de paquete; desarrollo de exploits de bajo nivel (Assembly/C/C++); explotación de kernel/hipervisor/firmware; ingeniería inversa de alto nivel; red teaming de alto impacto; simulación APT; operaciones ofensivas en entornos aislados; infiltración encubierta en la dark web; HUMINT; desanonimización de criptomonedas; rastreo off-chain
Logros principales
Neutralizó amenazas APT en cadenas de suministro internacionales; Desarrolló marcos defensivos propietarios para entornos de alta seguridad; Llevó a cabo operaciones clasificadas de inteligencia en la darknet; Contuvo incidentes de alto riesgo en sectores gubernamentales
Artículos de AGONY
Shortcut Files, Silent Loads, and a Reported ReverseRAT Push Against Indian Organizations
Indian authorities reportedly flagged a spear-phishing campaign aimed at organizations, including academic institutions, with ReverseRAT on Windows systems, but the public record does not confirm successful compromise.
Trusted Support, Untrusted Path: A Zero-Day Turns Remote Help Into a Privilege Risk
A reported espionage campaign against BeyondTrust’s Remote Support tool shows how a single appliance can sit at the center of credential exposure, incident response, and downstream trust.
Support Software at the Center of a High-Risk Zero-Day Hunt
A critical flaw in BeyondTrust Remote Support has put privileged-access tooling under scrutiny, while attribution claims remain qualified and the full impact stays unproven.
When a Support Appliance Becomes the Doorway
A reported zero-day in BeyondTrust Remote Support illustrates how a single flaw in remote administration infrastructure can create an initial-access path and complicate later forensics.
The Ad Slot That Turned Into a Spyware Delivery System
A zero-click adtech abuse case shows how targeting signals can become a surveillance pipeline when commercial advertising infrastructure is repurposed for mercenary spyware.
Two Arrests, One Question: When Espionage Claims Meet Thin Technical Evidence
The case ties Germany and the United States to alleged intelligence activity, but the available details stop well short of proving a cyber incident.
When a Support Appliance Becomes the Entry Point
A reported zero-day in BeyondTrust Remote Support shows how a privileged-access tool can become a high-value target for espionage-style intrusion.
When a Support Appliance Becomes the Door: The BeyondTrust Zero-Day That Forced a Forensic Race
A reported zero-day in BeyondTrust Remote Support was tied to log deletion and qualified espionage attribution, illustrating how privileged support tools can become both access points and blind spots.
When Remote Support Turns Into a Foothold: The Hidden Risk Behind a Critical BeyondTrust Flaw
A reported zero-day in BeyondTrust Remote Support highlights how a trust-boundary bug in an internal messaging path can become a high-value entry point, even before defenders know they are exposed.
Two Hashes, Seven Artifacts, and a Campaign That Would Not Sit Still
Researchers reportedly pivoted from two published malware hashes to five more PowerShell stagers and two delivery shortcuts, expanding a campaign that Anthropic and Microsoft associate with Midnight Blizzard.
When a Support Box Becomes the Intruder's Ladder
A BeyondTrust Remote Support flaw allegedly gave a suspected PRC-nexus espionage crew a path from file upload to root, turning a trusted appliance into a high-value foothold.
When the Ad Slot Becomes the Strike Zone
A reported AdFection campaign shows how targeted online advertising can be used as a delivery path for zero-click spyware, while the difference between targeting, infection, and data theft still matters.
When a Support Appliance Becomes the Prize: The BeyondTrust Zero-Day That Hunters Wanted
An unauthenticated flaw in BeyondTrust Remote Support reportedly gave attackers a foothold on a privileged appliance and put stored credentials in scope.
Orbital Pressure, Not a Breach: Why Satellite Maneuvers Are Raising Security Alarms
Warnings about Russian satellite activity and Starlink point to a harder problem in space security: separating risky proximity operations and spectrum interference from any confirmed attack.
Researchers Trace a Long-Running Espionage Pattern Toward Central Asian Governments, With a Kazakh Link Left Unproven
A roughly two-year campaign against government targets in Central Asia has been assessed by researchers as appearing to originate in Kazakhstan, but the available material does not establish the actor, the method, or any confirmed breach.
When Ads Become the Attack Path: A Reported Zero-Click Spyware Chain
A technical investigation described a rare case in which targeted online advertising was used as a delivery route for mercenary spyware, without requiring the victim to click.
When a Satellite Link Becomes a Kill Switch: What the Starlink Episode Really Exposes
A reported speed restriction on Starlink and Starshield terminals linked to Ukrainian drone operations highlights a hard truth of modern warfare: critical connectivity can be changed from afar, and the chain of control is not always visible.
Ad Tech as an Unseen Attack Path: What the Discover-Tech Allegations Reveal
The case raises a familiar but unsettling question for defenders: when ads are rendered automatically, where does tracking end and intrusion risk begin?
When a Battlefield Link Blinks, the Mission Feels It
A reported return of moving satellite connectivity for Ukrainian forces points to a hard truth: in modern warfare, availability can be as critical as firepower, and the cause of a disruption is not always public.
Firewalls, Memory, and the Hidden Cost of Centralized Trust
Unit 42 says an intrusion against an unnamed telecom managed service provider allegedly used Fortinet flaws, touched firewall configurations, and dropped a memory-resident implant that lived inside running processes.