


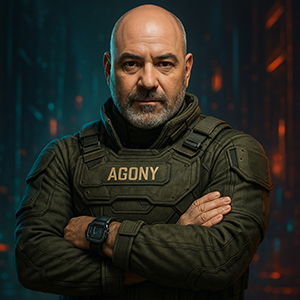
AGONY
Elite Offensive Security Commander
Professional Profile
Agony is the commander of one of the most advanced Ethical Hacking units operating across government and corporate environments. Considered a top-tier critical asset, he leads fifty elite specialists in high-risk operations, managing infrastructures, supply chains, and intelligence-driven missions. Active in variable multi-node contexts, he possesses extreme expertise in networking, exploit development, and deep-darknet operations.
Key Skills
Advanced enterprise/government networking; BGP manipulation & stealth routing; Zero-trust segmentation; Packet-level hardening; Low-level exploit development (Assembly/C/C++); Kernel/hypervisor/firmware exploitation; High-end reverse engineering; High-impact red teaming; APT simulation; Air-gapped offensive operations; Covert dark-web infiltration; HUMINT; Cryptocurrency de-anonymization; Off-chain tracing
Major Achievements
Neutralized APT threats in international supply chains; Developed proprietary defensive frameworks for high-security environments; Conducted classified darknet intelligence operations; Contained high-risk incidents in government sectors
Articles by AGONY
When a Keyboard App Became a Delivery Route for DarkVigil
A remote configuration request in Sogou Input Method reportedly became a malware path after network traffic was manipulated, showing how ordinary software features can carry outsized security risk.
AI as an Intrusion Multiplier: What the VAPOR PANDA Case Really Suggests
A reported espionage campaign points to a more operational use of AI, where agents are allegedly coordinated to run intrusion tasks in parallel under human direction.
How a Trusted Windows Input Tool Became a Malware Delivery Path
A reported abuse of Sogou Input Method’s brand-promotion and configuration workflow shows how ordinary software traffic can be turned into a spyware channel when network trust is weakened.
Invisible on the Wire: The Mobile Watering-Hole Playbook Returns
A reported campaign aimed at iOS and Android users shows how a trusted website can become a delivery point for exploit chains without proving that every visit became a compromise.
When the Attack Is on Judgment, Not Just Systems
A NATO science report treats decision-making itself as an attack surface, warning that digital technologies and AI can distort how organizations perceive, verify, and act on information.
Germany’s Spyware Warning Lands in a Gray Zone Between Suspicion and Proof
Some politicians and public figures in Germany were warned about possible spyware-related targeting, while earlier Apple notifications raised the same alarm without confirming a successful compromise.
Tax-Themed Phishing Puts Remote Access Software in the Spotlight
A reported campaign used fake Israel Tax Authority emails and disguised SimpleHelp files to test how far trust, not code, can carry an intrusion.
The WinRAR Trap Door That Could Turn a Routine Archive Into a Silent Beachhead
A Windows flaw in WinRAR has become a reminder that file extraction is a security boundary, while alleged campaign activity tied to it remains only partially verified.
The Quiet Trap in Trusted Scripts: How a Web Analytics Snare Can Shadow Mobile Users
A reported operation tied to APT29 shows why third-party JavaScript remains one of the web’s most fragile trust points, even when the exact compromise path is still unconfirmed.
When a Newsroom Goes Dark, the First Casualty Is Trust in the Pipe
The Kyiv Independent’s website was reportedly disrupted in a suspected Russian cyberattack, but the technical path, attribution, and any data impact remain unconfirmed.
When a Trusted Page Turns Hostile: The Mobile Watering-Hole Problem
A reported campaign aimed at iPhone and Android users shows how compromised websites and lookalike domains can blur the line between ordinary browsing and a possible attack path, even when no separate click is needed.
DNS Trickery Turned a Keyboard Tool into a Delivery Path
A reported hijack of Sogou Input Method’s network trust chain shows how insecure configuration traffic can be bent toward surveillance payload delivery without proving a full compromise.
Fake Front Doors, Real Risk: How a Mobile Watering Hole Turns Trusted Web Traffic Into a Trap
A reported campaign against iOS and Android users shows how compromised sites and cloned domains can put mobile browsers in the attack path without proving that any device was actually breached.
Propaganda, Synthetic Personas, and the MAGA Information War
A discussion of political disinformation around U.S. midterms highlights how AI, deepfakes, and “pink slime” sites can blur the line between persuasion and proof.
Gorbag and the Quiet War for Ukraine’s Credentials
A newly tracked espionage cluster reportedly focused on Ukrainian government, defense, and transport-linked targets shows how credential theft and archive abuse can matter as much as any noisy intrusion.
Missiles, Protest, and a Crypto Accusation: Why the Binance Story Is Bigger Than the Headline
North Korea’s latest missile launches arrived alongside a protest over U.S. claims tied to Binance, but the available record supports a geopolitical reading, not a proven technical link between the two.
The Job Offer Trap That Can Turn a Developer Laptop Into an Attack Path
A reported crypto intrusion tied to fake hiring, developer tools, and an unspecified internal AI system shows how recruitment workflows can become a security boundary.
Silent Pages, Loud Risk: The Mobile Trap Hidden in Trusted Browsing
A reported watering-hole campaign aimed at iPhone and Android users shows how a familiar website, a stale patch, and a zero-click chain can intersect without warning.
Inside the Hiring Trap: How a Crypto Giant’s Theft Claim Points to a Familiar Social-Engineering Playbook
Binance has linked a reported multibillion-dollar crypto theft to a months-long campaign and fake recruitment interviews, but the attribution and exact attack path remain contested.
Simple Malware, Sensitive Targets: The Cyber Shadow Over Ukraine’s Investigations and Aid Lines
A reported espionage campaign is said to target Ukrainian organizations tied to war-crimes work and military logistics, but the confirmed scope of access remains unclear.